
Polymarket says it has fixed the issue and referred it to law enforcement. Loss figures, the number of victims and the identity of the provider have not been confirmed though early reports are north of $2,000,000. This story is developing.
Oct. 29, 2026, about 2:40 p.m. ET.
Polymarket said on Thursday that one of its third-party providers was compromised in an incident affecting what it called its international platform, Polymarket.com. The company said it has referred the matter to law enforcement and that anyone impacted will be made whole. Trading is temporarily halted. The statement followed hours of user reports that funds and positions had left accounts without permission. On-chain trackers say a single wallet collected roughly $2.6 million in POL in under an hour. Polymarket has not given a loss figure or named the provider.
What Polymarket has said
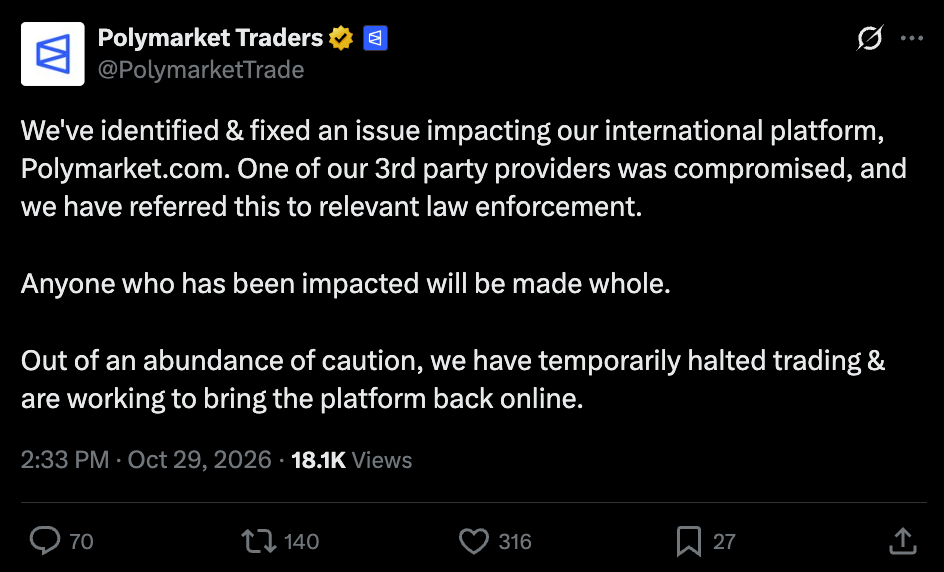
At 2:33 p.m. ET, the verified @PolymarketTrade account posted:
We've identified & fixed an issue impacting our international platform, Polymarket.com. One of our 3rd party providers was compromised, and we have referred this to relevant law enforcement.
Anyone who has been impacted will be made whole.
Out of an abundance of caution, we have temporarily halted trading & are working to bring the platform back online.
At 2:35 p.m. ET, the same text appeared as an @everyone announcement in Polymarket's official Discord server, posted by a user named Keaton | Polymarket who carries a Polymarket staff tag. The post links to the statement on X. The statement refers only to Polymarket.com and does not mention Polymarket US.
Polymarket's status page logged a major outage on its Predictions Trading API (CLOB) at 6:05 p.m. UTC (2:05 p.m. ET). The status page notice said the exchange was in cancel-only mode and relayer actions were paused while Polymarket investigated an incident. The status page also listed the web app, account login and on-chain settlement as operational.
The first reports
Aggr News relayed user reports of a possible site compromise at about 1:48 p.m. ET, according to FairGambling. The most widely shared first-hand account came from Car (@CarOnPolymarket), who posted at about 1:45 p.m. ET: "If you are a Polymarket user, lock down your account. I just got drained $800,000." He said a friend lost $600,000, later wrote that all of his positions were sold, and said the incident "looks like some sort of frontend hack maybe as multiple users are affected."
Car's claimed losses have not been confirmed, and some users dispute them. Trader @DidiTrading replied that Car had not been drained and had moved funds to one of his own wallets. X user @dimix111 wrote that Car was not actually drained but that the broader drain is real. Neither claim has been verified.
At 1:53 p.m. ET, @bernardbulletin quoted Car's post and wrote that traders were reporting a massive attack on Polymarket, with wallets reportedly drained for millions. PANews reported that other users described similar activity on X and in the Polymarket Discord, including one who said about $200,000 was taken and another who received an unauthorized withdrawal signature request on the official site.
What on-chain researchers report
Several analysts on X pointed to the same receiving address. At 2:26 p.m. ET, @TheBlockCo reported that Arkham data showed a wallet identified as the suspected attacker's held about $2.65 million in POL after receiving multiple USDC.e-to-POL swaps through Relay. Separately, Predict Time (@predicttime_) posted that Polymarket was in contact with the Relay team.
The crypto site defiprime, which is not an official account, published an analysis saying the address received its first POL at 1:10 p.m. ET and its last incoming transfer at 2:02 p.m. ET. It said the address held 28,636,284 POL, valued at about $2.64 million, at 2:19 p.m., and that none had moved as of 2:20 p.m. Defiprime counted 47 distinct addresses sending USDC or outcome tokens to the wallet and cautioned that the 47 senders are not a victim count.
Other accounts give different numbers. @AndrewSeb555 said about $2.6 million came from at least 33 accounts in 35 minutes. @TheFatMbappe said it had traced 2.724 million pUSD across 721 source wallets. @Lightsp2d put user-reported losses at about $1.4 million. A small account, @alphaXquant, claimed the attacker had accumulated $30 million; no other source supports that figure. Polymarket has confirmed none of these numbers.
Suspected cause
Several researchers on X point to a script from DebugBear, a website performance-monitoring company whose code ran on polymarket.com. At 2:00 p.m. ET, the verified @DebugBear account posted that the company was impacted by an ongoing security incident and asked customers using its RUM product to remove the embed code from their websites. The post does not mention Polymarket.
@0xRacerAlt described a malicious file served from a DebugBear CDN address. According to that post, the code read Polymarket login data stored in the browser and took over the user's active trading session. For email (Magic) accounts it sold positions without a wallet pop-up, and for external wallets it sent the user's position tokens to the attacker. Defiprime gave a similar account and said Polymarket's current site build includes a change titled "remove debugbear rum script," timestamped 1:59 p.m. ET. Polymarket's statement does not name the provider, and neither company has publicly linked the two.
At 2:30 p.m. ET, security firm PeckShield warned that Polymarket's UI may be compromised and told users not to interact with the site. Reports so far describe a website (frontend) problem. The reports cited here don't establish a flaw in Polymarket's smart contracts. Decrypt reported the cancel-only mode and outage notice. WuBlockchain wrote that users suspected a possible frontend compromise and that the cause remained unconfirmed.
Confirmed and unconfirmed
Confirmed by Polymarket or the provider:
One of Polymarket's third-party providers was compromised, affecting Polymarket.com, which the company calls its international platform.
Polymarket says it has identified and fixed the issue and referred it to law enforcement.
Polymarket says anyone impacted will be made whole.
Trading is temporarily halted. The status page has shown cancel-only mode and paused relayer actions since 2:05 p.m. ET.
DebugBear says it is affected by a security incident.
Reported, not confirmed:
That the compromised provider is DebugBear. Polymarket did not name it.
The total loss. On-chain trackers put it at about $2.6 million to $2.7 million at one wallet. Unverified claims go as high as $30 million.
The number of victims. Reports cite 33 accounts, 47 sending addresses and 721 source wallets, but those are different measures, not interchangeable victim counts.
Individual losses, including Car's $800,000 and his friend's $600,000. Car's claim is disputed.
Whether Polymarket US is affected. The statement names only Polymarket.com.
When trading will resume and how reimbursement will work.
Timeline (ET)
1:10 p.m.: The suspected attacker address receives its first POL (defiprime, on-chain data).
1:45 p.m.: Car posts that he was drained $800,000.
1:48 p.m.: Aggr News relays user reports of a possible site compromise (FairGambling).
1:53 p.m.: @bernardbulletin posts about the reports.
1:59 p.m.: A Polymarket site build removing the DebugBear script carries this timestamp (defiprime).
2:00 p.m.: DebugBear announces an ongoing security incident.
2:02 p.m.: The last incoming transfer reaches the suspected attacker address (defiprime).
2:05 p.m.: Polymarket's status page shows cancel-only mode and paused relayer actions.
2:26 p.m.: The Block reports Arkham data showing about $2.65 million in POL at the suspected attacker wallet.
2:30 p.m.: PeckShield warns users not to use the site.
2:33 p.m.: @PolymarketTrade says a third-party provider was compromised, the matter was referred to law enforcement, and impacted users will be made whole.
2:35 p.m.: Polymarket staff member Keaton posts the same statement to the official Discord.
Earlier incidents this year
On May 22, on-chain investigator ZachXBT flagged outflows from addresses tied to Polymarket's UMA CTF Adapter on Polygon. Estimates rose from about $520,000 to more than $660,000. Polymarket said findings pointed to a private key compromise of a wallet used for internal top-up operations, not its contracts or core infrastructure, and said user funds and market resolution were safe.
On June 25, Polymarket said a third-party vendor had been compromised, injecting a malicious script into its frontend for some users, and promised full refunds. AMLBot and CoinDesk reported about $3.1 million taken from 11 wallets. Polymarket has not said whether the June vendor and Thursday's provider are connected. Some posts on Thursday describe the June incident as if it were happening today.
This article includes a link to PredictQ partner Polymarket. We may earn a commission if you use it. That doesn't cost you anything extra, and it helps keep the lights on here. Nothing in this piece is investment advice, and prices, odds, and entry counts can change.